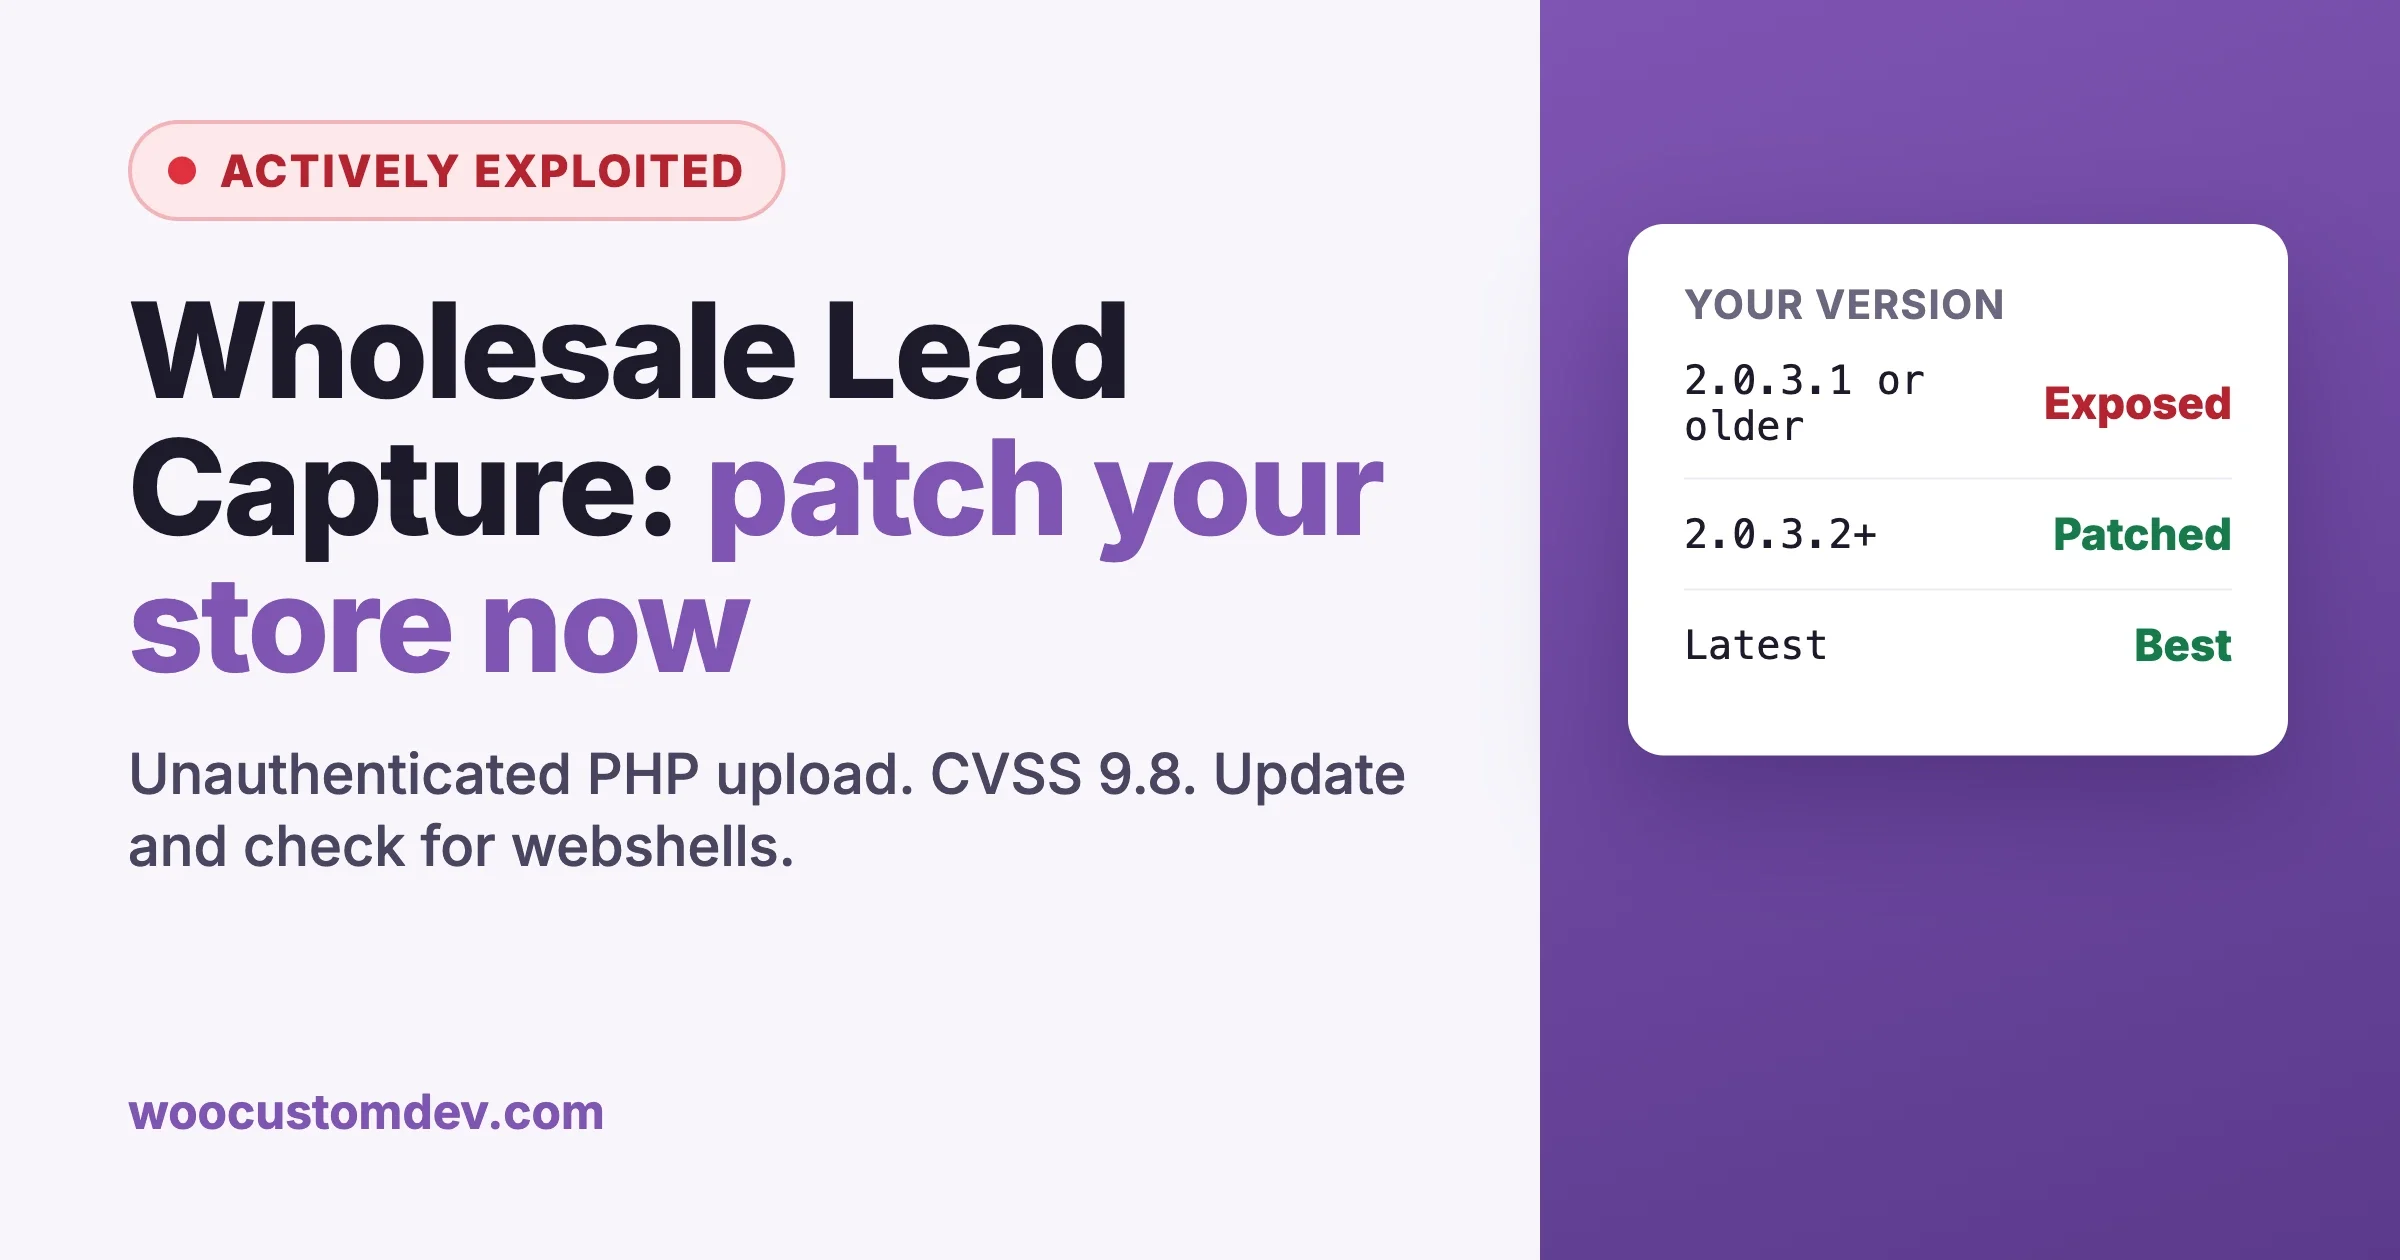
WooCommerce Wholesale Lead Capture Vulnerability: Patch Now
A critical unauthenticated file upload bug in WooCommerce Wholesale Lead Capture (CVE-2026-27540) is under active attack. How to check your store, patch, block it, and spot a webshell.
The largest section here. Checkout and payments, shipping and tax, B2B pricing, integrations, and the operational work that starts the day after launch. Written while fixing real stores, so the emphasis falls on what breaks rather than what demos well.

A critical unauthenticated file upload bug in WooCommerce Wholesale Lead Capture (CVE-2026-27540) is under active attack. How to check your store, patch, block it, and spot a webshell.

How products, variations and plugins are set up before the store becomes hard to change.
Read onConnecting a store to a CRM, ERP or fulfilment provider, and planning for the failed sync.
Read onLife after launch: order edits, refunds, stock drift and the reports rebuilt every Monday.
Read onThe all-in-one WordPress community stack
Also ours: wbcomdesigns.comvapvarun.combrndle.com